
Logging · head to head
Honeycomb vs Splunk Cloud
Splunk Cloud
Logging
Cloud-Based Log Management and Analytics
- From
- $675/year
- Free plan
- No
The short version
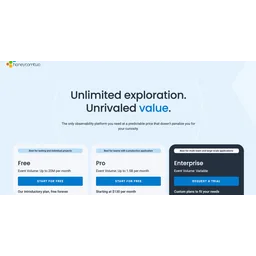
- Honeycomb has a free plan, then $150/mo; Splunk Cloud starts at $675/yr.
- Where Honeycomb falls short: free tier caps at 20 million events per month and 100 million metrics data points.
- Where Splunk Cloud falls short: significantly higher pricing than competitors like Datadog and Elastic.
- Prices and features on this page were last checked on 13 November 2026.
Where they differ
Only the attributes on which Honeycomb and Splunk Cloud actually diverge.
| Attribute | Honeycomb | Splunk Cloud |
|---|---|---|
| Starting price | Free | $675/year |
| Free tier | Yes | No |
Identical on both: platforms (Web), category (Logging).
Not yet recorded: pricing model for Splunk Cloud, founded for Honeycomb.
What each one covers
Drawn from each product's published feature list. An absence here means we hold no record of it - not that the product lacks it.
Only in Honeycomb
Nothing recorded that Splunk Cloud does not also cover.
Only in Splunk Cloud
- Log aggregation
- Real-time analytics
- Machine learning
- Advanced dashboards
- Compliance tools
- Cloud scalability
- API
- Webhooks
What people use each for
The jobs each tool is most often brought in to do.
Honeycomb
- Tracing requests through distributed microservicesnot Splunk Cloud
- Observing AI agent behavior in productionnot Splunk Cloud
- Debugging cloud migrations in real-timenot Splunk Cloud
- Monitoring Kubernetes across multiple cloudsnot Splunk Cloud
Splunk Cloud
- Log monitoringnot Honeycomb
- Application performancenot Honeycomb
- Security analyticsnot Honeycomb
- Troubleshootingnot Honeycomb
Where each one falls short
Documented limitations, not opinions. Every one is a constraint you would hit in normal use.
Honeycomb
- Free tier caps at 20 million events per month and 100 million metrics data points
- Pro tier starts at $150 per month for only 50 million events, with cost scaling per additional event block up to its 750 million event ceiling
- Enterprise tier's event and data point volumes are variable and its price is custom, requiring direct sales contact
- Telemetry Pipeline is billed separately at $0.10 per GB on top of the base plan price
Splunk Cloud
- Significantly higher pricing than competitors like Datadog and Elastic
- Per-GB ingest costs of $150+/day make budget forecasting difficult
- Extended retention adds substantial additional costs
- Enterprise Security add-on costs $25-45/GB/day on top of base pricing
Pricing, plan by plan
Honeycomb
Free- FreeFree
- 20M events per month
- 100M metrics data points per month
- 2 Triggers
- Pro$150/mo
- 750M events per month
- 3.75B metrics data points per month
- 100 Triggers
Splunk Cloud
$675/yearNo published plan breakdown. See the Splunk Cloud review.
Which should you pick?
Choose Splunk Cloud if
- You need log aggregation.
- You also want real-time analytics.
Questions people ask
- Is Honeycomb or Splunk Cloud better?
- Neither clearly leads. Honeycomb starts at Free and Splunk Cloud at $675/year, and user ratings are close enough to be indistinguishable. Choose on capability and platform support.
- Which is cheaper, Honeycomb or Splunk Cloud?
- Honeycomb has a free tier; the other does not. Paid plans start at Free for Honeycomb and $675/year for Splunk Cloud.
- Does Honeycomb or Splunk Cloud run on more platforms?
- Both run on Web, so platform support will not decide this one for you.
- Can I use Honeycomb for free?
- Yes. Honeycomb has a free tier, so you can try it without paying. Splunk Cloud starts at $675/year.
- What is Honeycomb best used for?
- Honeycomb is most often used for tracing requests through distributed microservices, observing ai agent behavior in production, debugging cloud migrations in real-time, monitoring kubernetes across multiple clouds. Of those, tracing requests through distributed microservices and observing ai agent behavior in production are not what Splunk Cloud is typically brought in for.
- What can Honeycomb do that Splunk Cloud cannot?
- Splunk Cloud covers Log aggregation, Real-time analytics, Machine learning, Advanced dashboards.
Answered from the vendors’ own pages
Honeycomb: Is Honeycomb free forever?
Honeycomb offers a free plan forever with up to 20M events per month and 100M metrics data points per month, best for testing and individual projects.
SourceSplunk Cloud: How is Splunk Cloud priced?
Splunk Cloud uses two pricing models: legacy per-GB ingest at $150+/GB/day or newer workload pricing ranging from $3,000 to $400,000/month depending on pack size. Simpler deployments offer ingest pricing with 5GB/day at $675/year.
SourceHoneycomb: What is the cost of Honeycomb's Telemetry Pipeline?
Honeycomb's Telemetry Pipeline starts at $0.10 per GB, with monthly or annual billing options available.
SourceSplunk Cloud: What is included with Splunk Cloud storage?
Storage is included for a default retention period, typically 90 days for hot/warm data, with extended retention costing extra.
SourceHoneycomb: Can I get custom Honeycomb pricing?
Yes, Honeycomb offers Enterprise plans with custom pricing and a base allowance starting at 10 billion events per year with dedicated support.
SourceSplunk Cloud: Is Splunk Cloud managed or do I need to manage infrastructure?
Splunk Cloud is a fully managed SaaS offering where Cisco (current owner) handles infrastructure, upgrades, and scaling.
SourceSplunk Cloud: What makes Splunk Cloud expensive compared to alternatives?
Splunk remains the highest-priced major log platform, but offers the most powerful query language (SPL) and the deepest enterprise security ecosystem.
SourceRelated pages
More on Splunk Cloud
Other head to heads
- Honeycomb vs Better Stack
- Honeycomb vs Coralogix
- Honeycomb vs Datadog
- Honeycomb vs InfluxDB
- Honeycomb vs Checkmk
- Honeycomb vs Rollbar
- Honeycomb vs Site24x7
- Honeycomb vs Traceloop
- Honeycomb vs New Relic
- Honeycomb vs Elastic Stack
- Honeycomb vs Bugsnag
- Honeycomb vs Dynatrace Logs
- Honeycomb vs Datadog Logs
- Honeycomb vs Telegraf
- Honeycomb vs Elastic
- Honeycomb vs Elastic APM
- Honeycomb vs Elasticsearch Service
- Honeycomb vs ELK Stack
- Honeycomb vs CloudWatch
- Honeycomb vs Graylog
- Honeycomb vs Loggly
- Honeycomb vs Logz.io
- Honeycomb vs Sumo Logic
- Honeycomb vs Grafana Loki
- Honeycomb vs Sentry
- Honeycomb vs LogRocket
- Honeycomb vs Axiom
- Splunk Cloud vs Better Stack
- Splunk Cloud vs Coralogix
- Splunk Cloud vs Datadog
- Splunk Cloud vs InfluxDB
- Splunk Cloud vs Checkmk
- Splunk Cloud vs Rollbar
- Splunk Cloud vs Site24x7
- Splunk Cloud vs Traceloop
- Splunk Cloud vs New Relic
- Splunk Cloud vs Elastic Stack
- Splunk Cloud vs Bugsnag
- Splunk Cloud vs Dynatrace Logs
- Splunk Cloud vs Datadog Logs
- Splunk Cloud vs Telegraf
- Splunk Cloud vs Elastic
- Splunk Cloud vs Elastic APM
- Splunk Cloud vs Elasticsearch Service
- Splunk Cloud vs ELK Stack
- Splunk Cloud vs CloudWatch
- Splunk Cloud vs Graylog
- Splunk Cloud vs Loggly
- Splunk Cloud vs Logz.io
- Splunk Cloud vs Sumo Logic
- Splunk Cloud vs Grafana Loki
- Splunk Cloud vs Sentry
- Splunk Cloud vs LogRocket
- Splunk Cloud vs Axiom